


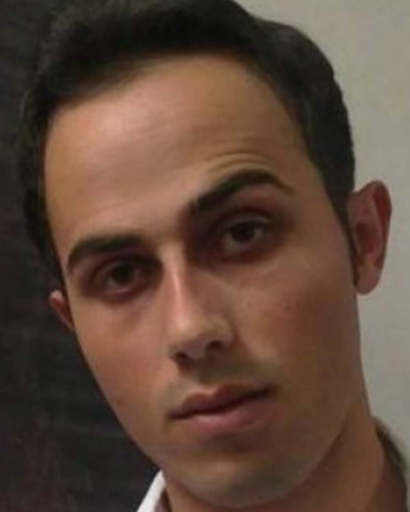
Biographical details:
Balujeh is Iranian and lives in Iran. He was born on April 20 1988 in Mianeh.
No widely known hacking alias has been publicly associated with him and no prominent standalone case has centered on his name.
He has been associated with MOIS, Net Peygard Samavat, Mabna Institute and APA Security.
His last known address is Tehran, Sheikh Bahaii Shomali, Koucheh Dawazdeh Metri Sevom, Plak 14, Vahed 2, Code Posti 1995873361, Iran.
Summary of activities within Iranian Cyber Operations:
Balujeh is a malicious cyber actor sponsored by Iran’s Ministry of Intelligence and Security. He has participated in hacking and data exfiltration operations against the U.S and its allies to the benefit of the Iranian government. has left a smaller public footprint than the other four hackers.
Despite the fact Balujeh appears to have left a smaller public footprint than Kahzadian, Mesri, Ghaleh-Kuhi and Fayyaz, according to a US indictment his operational role in Mabna and Project Sonbol was still extensive.
Balujeh worked from August 2013 at an APA cybersecurity center that provided hacking services to MOIS under contract. He later moved to Mabna, participating in phishing, data takeovers, data extraction, attacks against private companies and the HBO operation.
After the 2018 indictment, he joined Project Sonbol. From October 2018 through to March 2022, he worked independently and alongside Fayyaz and Ghaleh-Kuhi, using passwords spraying to penetrate private companies and at least two U.S government agencies. In some cases the hackers transferred terabytes of stolen data to accounts they controlled.
Their targets spanned the defense, energy, technology, media transportation, healthcare and government sectors. During some operations, stolen credentials and data were offered for sale on the dark web. Fayyaz acted as a seller under various aliases while Balujeh participated in password spraying, intrusion and data extraction.
By 2023, Balujeh was part of a group managed by Mesri and Ghaleh-Kuhi that repeatedly carried out network intrusions for or on behalf of Iran’s Intelligence Ministry.
In 2024, Balujeh, Fayyaz and Kadkhodaei successfully penetrated several local, state and federal government agencies across the U.S. He was also involved in an Iranian telecommunications company attack in 2025, penetrating its systems and extracting data.
Key Incidents and Attribution:
Balujeh has worked for the Mabna Institute. From October 2018 to March 2022, Balujeh and other cyber actors conducted a hacking campaign as part of a MOIS directed effort known as the “Senabel Project”. Under this project the malicious cyber actors stole terabytes of proprietary data from several U.S entities that was exfiltrated to online accounts. Victims include a U.S information technology firm, three U.S based defense contractors, a U.S based energy company, an airline, and several other entities.
Since 2022, Balujeh and his associates have targeted a variety of critical infrastructure sectors, including healthcare, defense, energy, and finance, often using hacking, brute force attacks, and the exploitation of vulnerabilities in systems and networks to gain unauthorized access to sensitive information.
International Recognition & Legal Actions
US Criminal Indictments and Arrest Warrants:
He has been indicted twice by the U.S Department of Justice for computer intrusion activity against U.S and worldwide entities.
On the 18 August 2026, the U.S Department of Justice “Rewards for Justice” program announced that it is offering a reward of up to $10 million for information leading to the identification or location of any person who, while acing at the direction or under the control of a foreign government, participates in malicious cyber activities against U.S critical infrastructure in violation of the Computer Fraud and Abuse Act.
The U.S Department of Justice unveiled the 14-count superseding (S2) indictment charging 17 members of the Mabna Institute, including Balujeh. The superseding indictment alleged that, at the behest of entities including the IRGC, these defendants hacked into universities and other research institutions worldwide, including the United States, stealing at least 31 terabytes of information and intellectual property of untold value.
Sanctions and Designations: The U.S Treasury released a press release on the 24 August 2026 announcing a fresh wave of sanctions against more than 60 officials, entities, and networks linked to Iran’s military, cyber, and oil trading activities. These sanctions included Balujeh and other members of the Mabna Institute.
