

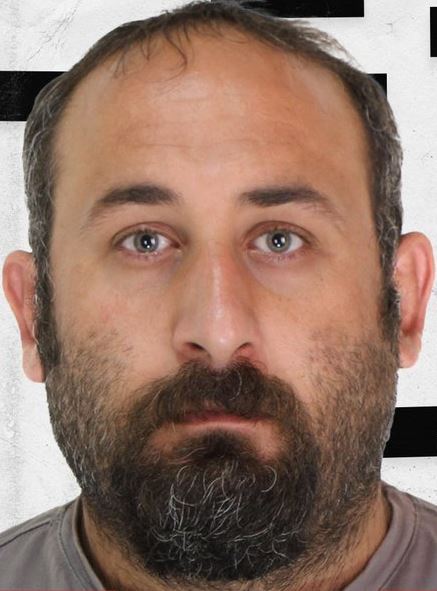

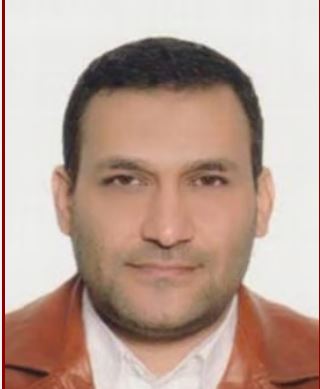
Behzad Mesri is an Iran-based hacker and former CEO of the Net Peygard Samavat Company (later rebranded as Emennet Pasargad). He is publicly accused, by the US, of conducting high‑profile intrusions, data theft, extortion, and participating in state‑aligned malicious cyber campaigns tied to the Islamic Republic of Iran. Mesri is part of the broad ecosystem supporting Islamic Revolutionary Guard Corps (IRGC) linked cyber operations.
Biographical Details
- Mesri lives in Iran, is Iranian, and was born on August 24 1988 in Naghadeh, Iran. He is known to speak Persian and some English.
- In 2017, Mesri was understood to be 5’9″ with brown hair, brown eyes, and weighed roughly 80kg.
- Mesri is a self-professed expert in computer hacking techniques.
- Mesri has operated under the online pseudonyms of “Mr Smith” and “Skote Vahshat”, meaning “The Silent Terror.”
Summary of activities within Iranian Cyber Operations
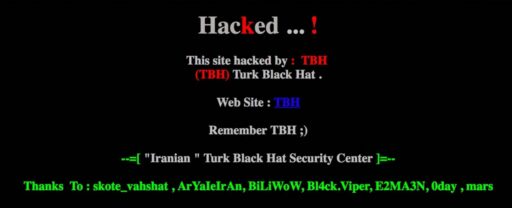
Mesri was first linked to the Iran-based hacking group “Turk Black Hat Security Team” in 2008 conducting website defacements and other activities inside and outside of Iran. Mesri co-founded Black Hat Security with Manouchehr Hashemloo.
Mesri then joined Unit 2000 of the IRGC IO in 2013 where he worked alongside Hashemloo and Fayyaz on operations targeting military systems, software related to Israel’s nuclear program and Israel infrastructure.
He then joined Net Peygard Samavat in May 2014 where he served as CEO and was a board member of the company. During this time he worked alongside fellow hackers Hashemloo and Ghaleh-Kuhi. Mesri also used information by Monica Witt, a former U.S Air Force counterintelligence officer who defected to Iran, to provide servers and technical infrastructure for operations against current and former U.S Air Force counterintelligence personnel. He managed fake accounts, phishing and malware delivery in the campaign. Mohammad-Bagher Shirinkar, also known as Mojtaba Tehrani, was identified as the company’s technical director and during his time at the company he coordinated contacts with the IRGC and reported on project progress to IRGC officials.
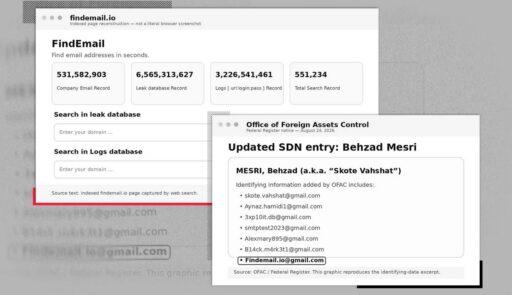
Mesri subsequently contracted with Mabna, that is known to be strongly linked to the Iranian Ministry of Intelligence and Security (MOIS). Here he was responsible for managing infrastructure and distributing stolen credentials. He and Ghaleh-Kuhi also established findmail.io, which was allegedly used to sell stolen credentials for private profile.
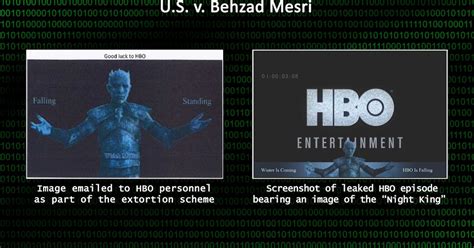
In 2017, he was linked to the cyber-attack against HBO (the American media organization, Home Box Office Inc.). Mesri later served as CEO of the Net Peygard Samavat Company which has been linked to the Islamic Revolutionary Guard Corps Cyber Electronic Command (IRGC-CEC).
Since 2022, despite repeated electricity shortages affecting ordinary Iranians, Mesri has allegedly operated an energy-intensive cryptocurrency mining operation in Naqadeh with privileged access to cheap electricity.
Key Incidents & Attribution
- Turk Black Hat Security Team: Mesri was involved in conducting hundreds of website defacements under the alias “Silent Terror,” targeting sites in the United States and elsewhere. US attributions also link him to activity against military systems, nuclear software, and Israeli infrastructure.
- HBO Intrusion and extortion (May-August 2017): US prosecutors allege Mesri conducted online reconnaissance beginning in May 2017, compromised multiple HBO employee accounts, and exfiltrated roughly 1.5 terabytes of proprietary data (including unaired video files and scripts/plot summaries for programs such as Game of Thrones, Barry, Ballers, Room 104, and more). Mesri sent ransom and threatening emails demanding about $5.5-6 million in Bitcoin, and publicly leaked the data when demands were not met. Mesri’s first email to HBO staff stated, among other things, “Hi to All losers! Yes it’s true! HBO is hacked! … Beware of heart Attack!!!”
- Net Peygard Samavat – Mesri as CEO: While CEO, Mesri is alleged to have overseen the acquisition of servers and operational activities aimed at gaining access to and implanting malware on devices of current and former U.S. counterintelligence personnel.
- Net Peygard Samavat – Election Activities (August-November 2020): The US Treasury states the company led online operations to intimidate and influence American voters, including attempts to obtain voter information from state websites, sending threatening emails, and crafting/disseminating disinformation about the election and election security.
International Recognition & Legal Actions
- US Criminal indictments and arrest warrants: A Southern District of New York indictment (8 November 2017) charged Mesri with computer fraud, wire fraud, extortion‑related offenses, and aggravated identity theft. A District of Columbia indictment (8 February 2019) charged Mesri with conspiracy, attempted intrusions, and aggravated identity theft. Federal arrest warrants have been issued.
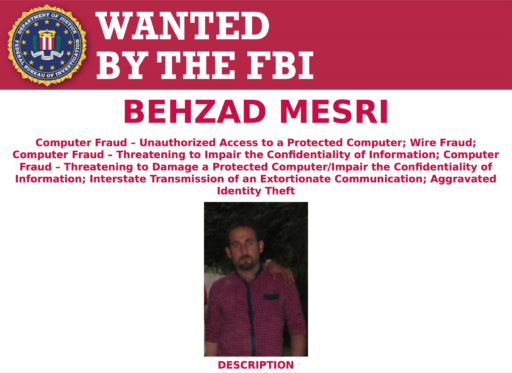
- FBI WANTED notice: Mesri is wanted by the US Federal Bureau of Investigation (FBI) for computer fraud, fraud, wire fraud, interstate transmission of an extortionate communication, and aggravated identity theft.
- Sanctions and Designations: Mesri is designated under Executive Order 13694 for his role in the HBO attack. He is also designated under E.O 13606 for his connection to the Net Peygard Samavat Company. The company is sanctioned under the same designation for providing support to the IRGC Electronic Warfare and Cyber Defense (IRGC-EWCD) organization and for its 2020 election‑related activities. Mesri is subject to secondary sanctions.
- On the 18 August 2026 the U.S Department of Justice unveiled a 14-count superseding (S2) indictment charging 17 members of the Mabna Institute, including Mesri. The superseding indictment alleged that, at the behest of entities including the IRGC, these defendants hacked into universities and other research institutions worldwide, including the United States, stealing at least 31 terabytes of information and intellectual property of untold value.
- The U.S Treasury released a press release on the 24 August 2026 announcing a fresh wave of sanctions against more than 60 officials, entities, and networks linked to Iran’s military, cyber, and oil trading activities. These sanctions included Mesri and other members of the Mabna Institute.
