


Biographical details:
- Fayyaz is Iranian and lives in Iran. He was born in December 18, 1989 in Mianeh.
- He is known by the following online aliases: Keyvan Karimi, Hurr!c4nE!, k3yv4n, b.cmonster, fokonishi, Achilles, Chikoo, JakJak, the.joker. hensi, Team XXXX.
Summary of activities within Iranian Cyber Operations:
Fayyaz’s hacking campaign started in 2010 when he co-founded the Ajax Security Team. He initially built his reputation by identifying vulnerabilities, publishing security tools and defacing websites, including Iranian government sites. By 2012 Ajax’s activities became more political and its members participated in campaigns including OpIsrael and OpUSA.
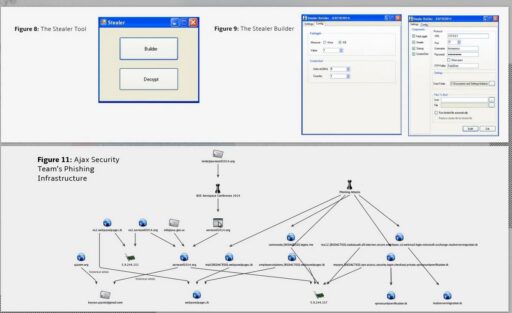
He was allegedly recruited by the IRGC IO in late 2012 after becoming aware of his hacking potential. As Fayyaz began working with Unit 2000, Ajax’s public defacement activity declined and the group developed into a malware-based cyber-espionage operation.
Fayyaz worked for the IRGC IO until late 2016, developing ties with Mesri and other state-linked cyber operatives. After he left he registered Imen Faraz Rayan Ghaflan in Mianeh in January 2017. Subsequently, Fayyaz moved to the Mabna Institute. From 2018, Fayyaz joined Project Sonbol where he worked under Mesri and Ghaleh-Kuhi and alongside Shahbazi and Mohammadreza Kadkhodaei. From 2020, his independent criminal activity expanded and using at least six aliases, he entered illicit forums and markets and sold credentials belonging to compromised companies and individuals. Fayyaz developed into an “initial-access broker” — a hacker who compromises an organization and sells the foothold to other criminal groups.
Key Incidents and Attribution:
The FBI has stated that Fayyaz was recruited to join the IRGC IO Department 2000, where he conducted malicious cyber operations against the U.S and foreign defense organizations and various Israeli targets across several sectors.
Following employment with the IRGC IO, Fayyaz worked for the Mabna Institute, which was founded by two U.S-indicted MOIS cyber officers. The Mabna Institute conducted a massive spear phishing and intellectual property campaign targeting U.S and other professors and universities worldwide on behalf of the IRGC.
As a Mabna Institute employee, Fayyaz was involved in the hack and extortion of the U.S entertainment company HBO at the behest of the IRGC and participated in hacking operations targeting several U.S defense companies, a U.S communications technology provider, a Saudi energy company, and others.
International Recognition & Legal Actions
US Criminal Indictments and Arrest Warrants:
In 2020, U.S authorities indicted Fayyaz for his malicious activities conducted while working for the Mabna Institute.
On the 18 August 2026, the U.S Department of Justice “Rewards for Justice” program announced that it is offering a reward of up to $10 million for information leading to the identification or location of any person who, while acing at the direction or under the control of a foreign government, participates in malicious cyber activities against U.S critical infrastructure in violation of the Computer Fraud and Abuse Act.
The U.S Department of Justice unveiled the 14-count superseding (S2) indictment charging 17 members of the Mabna Institute, including Fayyaz. The superseding indictment alleged that, at the behest of entities including the IRGC, these defendants hacked into universities and other research institutions worldwide, including the United States, stealing at least 31 terabytes of information and intellectual property of untold value.
Sanctions and Designations: The U.S Treasury released a press release on the 24 August 2026 announcing a fresh wave of sanctions against more than 60 officials, entities, and networks linked to Iran’s military, cyber, and oil trading activities. These sanctions included Fayyaz and other members of the Mabna Institute.
