

APT Iran
Affiliation: Iran APT appears to be a pro-Iran and pro-regime hacktivist group, though exhibiting a notable shift in allegiance. Originally identified as “APT Iran Research Center” or «مرکز تحقیقات APT IRAN» and appearing anti-regime in early 2024, the group now…
Gorz Rostam
Gorz Rostam is a politically motivated pro Iran threat actor that has gained notoriety in recent months for its Distributed Denial of Service (DDoS) attacks against targets across Israel, Qatar, the UAE, Bahrain, and Europe. Their name, “Rostam’s mace”, which…
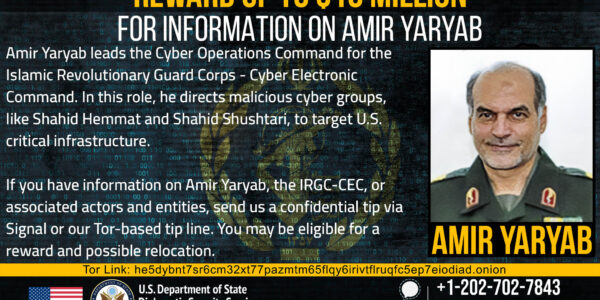
Amir Yaryab
Biographical details: Amir Yaryab is Iranian. Summary of activities within Iranian Cyber Operations: Yaryab is the Head of Cyber Operations Command for the Islamic Revolutionary Guard Corps. In this role he directs malicious cyber groups, such as Shahid Hemmat, Shahid…
Arman Kahzadian
Biographical details: Arman Kahzadian is Iranian and lives in Iran. He was born in February 11 1992 in Ilam. He has been affiliated with the IRGC, MOIS, Mabna Institute, Digital Boys Underground Team, APA Security and Imen Wall Pardaz. He…
Saber Shahbazi Balujeh
Biographical details: Balujeh is Iranian and lives in Iran. He was born on April 20 1988 in Mianeh.No widely known hacking alias has been publicly associated with him and no prominent standalone case has centered on his name. He has…
Mojtaba Ghaleh-Kuhi
Biographical details: Ghaleh-Kuhi is Iranian and lives in Iran. He was born on June 28 1988 in Naqadeh. He has been associated with the IRGC-CEC, IRGC Qods Force (IRGC-QF), Ministry of Intelligence and Security (MOIS), Eeleyanet Gostar Iraniyan aka Net…
Keyvan Fayyaz Ghareh Blagh
Biographical details: Summary of activities within Iranian Cyber Operations: Fayyaz’s hacking campaign started in 2010 when he co-founded the Ajax Security Team. He initially built his reputation by identifying vulnerabilities, publishing security tools and defacing websites, including Iranian government sites….

Mabna Institute
Mabna Institute is an Iranian Advanced Persistent Threat (APT) group active since 2013, focused on the theft of research data, intellectual property, and credentials from universities, government agencies, and private sector organizations. Primarily motivated by financial gain, the group has…
Imperial Kitten
List of names used by the industry: Date founded: The group have been active since at least 2017 but was first reported in September 2019. Affiliation: Iran-nexus “threat cluster” that is linked to the Islamic Revolutionary Guard Corps (IRGC). Social…
Nimbus Manticore
List of names used by industry: Date founded:The group is believed to have been active since June 2022. Affiliation:The group has been affiliated with the Islamic Revolutionary Guard Corps and overlaps with other Iranian hacking groups such as Crimson Sandstorm.Nimbus…