

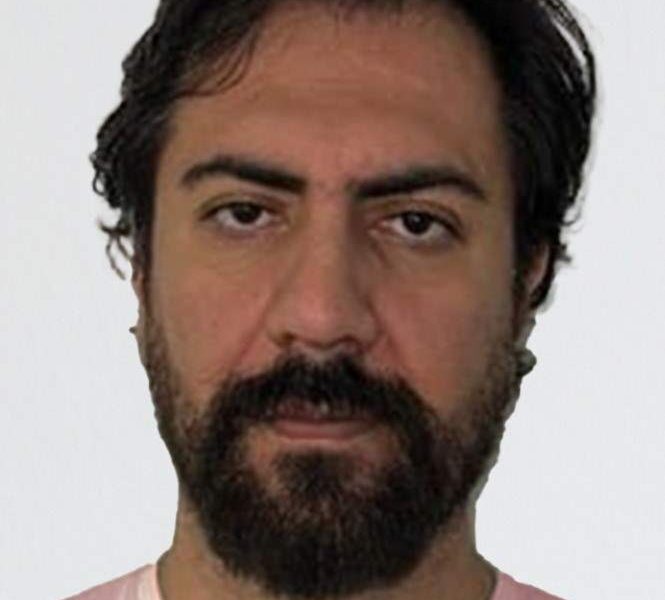

Biographical details:
Ghaleh-Kuhi is Iranian and lives in Iran. He was born on June 28 1988 in Naqadeh. He has been associated with the IRGC-CEC, IRGC Qods Force (IRGC-QF), Ministry of Intelligence and Security (MOIS), Eeleyanet Gostar Iraniyan aka Net Peygard Samavat aka Emennet Pasargad aka Aria Sepehr Ayandehsazan and Mabna Institute.
Ghaleh-Kuhi previously operated under the aliases mb_1986, mb_1986m and Mosi PC.
Summary of activities within Iranian Cyber Operations:
Ghaleh-Kuhi is a malicious cyber actor sponsored by Iran’s Ministry of Intelligence and Security. He has participated in hacking and data exfiltration operations against the U.S and its allies to the benefit of the Iranian government.
In 2013 he was active in Iran’s website-defacement community and links one of his aliases to the network later known as “Flying Kitten”, which evolved from website defacement and underground forums to spear phishing, credential theft and cyber espionage. Later, Mojtaba Borhani and Ghaleh-Kuhi were both linked to Flying Kitten and Charming Kitten. It is possible he was contracting for Imem Wall Pardaz during this period.
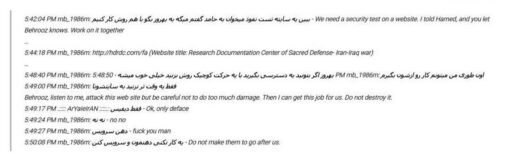
Between late 2013 and the summer of 2014, Ghaleh-Kuhi inadvertently uploaded six months of private conversations with Hashemloo to VirusTotal, an online cybersecurity analysis platform. The conversations provided a direct link between Fayyaz and Ghahleh-Kuhi and also showed the team recruiting staff, acquiring servers later used in espionage attempts against members of Iran’s human rights community and discussing connections within the security establishment.
Ghaleh-Kuhithen joined Mabna in 2016 and later became one of the central figures in Project Sonbol, managing infrastructure and directing operations.
Ghaleh-Kuhi appears to make a formal appearance in 2016 when he joined the cyber company Ilya Net Gostar Iranian. At Ilya Net, Ghaleh-Kuhi’s work was supervised by Mohammad-Bagher Shirinkar, then known as Mojtaba Tehrani. Mesri and Hashemloo were among his close associates.
Key Incidents and Attribution:
As early as 2014, Ghaleh-Kuhi worked at the front company Ilya Net conducting computer network operations and social engineering to benefit the IRGC QF and the IRGC CEC. Specifically, Ghaleh-Kuhi helped develop an indigenous tool used to gather intelligence used in social engineering against IRGC targets of interest.
Following his employment with Ilya Net, he was recruited to work for the Mabna Institute.
Ghaleh-Kuhi is said to have been part of a hacking campaign as part of a MOIS directed effort known as the “Senabel Project”. Under this project the malicious cyber actors stole terabytes of proprietary data from several U.S entities that was exfiltrated to online accounts. Victims include a U.S information technology firm, three U.S based defense contractors, a U.S based energy company, an airline, and several other entities.
International Recognition & Legal Actions
US Criminal Indictments and Arrest Warrants:
Ghaleh-Kuhi was indicted by the U.S Department of Justice and sanctioned (find more of sanction) by the U.S Department of the Treasury for the targeting of victim organizations through computer network exploitation and intrusion.
On the 18 August 2026, the U.S Department of Justice “Rewards for Justice” program announced that it is offering a reward of up to $10 million for information leading to the identification or location of any person who, while acing at the direction or under the control of a foreign government, participates in malicious cyber activities against U.S critical infrastructure in violation of the Computer Fraud and Abuse Act.
The U.S Department of Justice unveiled the 14-count superseding (S2) indictment charging 17 members of the Mabna Institute, including Ghaleh-Kuhi. The superseding indictment alleged that, at the behest of entities including the IRGC, these defendants hacked into universities and other research institutions worldwide, including the United States, stealing at least 31 terabytes of information and intellectual property of untold value.
Sanctions and Designations: The U.S Treasury released a press release on the 24 August 2026 announcing a fresh wave of sanctions against more than 60 officials, entities, and networks linked to Iran’s military, cyber, and oil trading activities. These sanctions included Ghaleh-Kuhi and other members of the Mabna Institute.
