


Gorz Rostam is a politically motivated pro Iran threat actor that has gained notoriety in recent months for its Distributed Denial of Service (DDoS) attacks against targets across Israel, Qatar, the UAE, Bahrain, and Europe. Their name, “Rostam’s mace”, which evokes the figure from Persian mythology, suggests a possible geopolitical motivation, although the group has not issued clear political demands.
List of names used by the industry:
Gorz Rostam
Rostam’s mace
Date founded:
The group created its Telegram channel on March 19.
Social media handles:
Telegram: t.me/GORZROSTAM313
t.me/Forum_Shop_Rostam
X: @GORZROSTAM313
Previous Operations:
Gorz Rostam’s operations began in March 2026.
- March 21: DDoS attack carried out against tuv-haaretz.co.il, evenniar.co.il, alumatt.co.il, and seakayak.co.il.
- March 22: DDoS attack carried out against ita.co.il. DDoS attack carried out against the Dubai Police UAE website.
- March 24: DDoS attack carried out against the Qatar government services portal.
- March 26: DDoS attack carried out against accessnet.co.il.
- March 27: DDoS attack carried out against Energean (www.energean.com), an international oil and gas company operating in Israel.
- March 29: DDoS attack carried out against ilya.shalumov.co.il.
- March 31: DDoS attack carried out against an Abu Dhabi-based UAE telecom company (offering mobile, home internet, TV, and business/digital services), Dubai’s electricity and water provider (www.dewa.gov.ae), and Euroline.co.il.
- April 1: DDoS attack carried out against Bahrain’s General Directorate of Customs Information.
- April 2: DDoS attack carried out against eitan-ur-co.il and Khalifa University Abu Dhabi.
- April 5: DDoS attack carried out against the Qatar Chamber and Go1.co.il.
- April 7: DDoS attack carried out against The Kingdom of Bahrain’s sovereign wealth and investment company.
- April 8: DDoS attack carried out against an international investment firm headquartered in Bahrain, a Qatar Bank, and various Israeli websites and UAE online systems.
- April 10: DDoS attack carried out against the Federation of Israeli Sports and the Daily Daf Yomi (Talmud study) website.
- April 11: DDoS attack carried out against News of Bahrain, Habsor.co.il, Spinplus.co.il, Ron-shpatz-cohen.co.il, and Ronazohar.co.il.
- April 13: DDoS attack carried out against blog.cepgranada.org.
- April 14: DDoS attack carried out against thirdage.co.il.
- April 18: DDoS attack carried out against a USA-based system that controls and monitors HVAC, boilers, and gas systems.
- April 19: DDoS attack carried out against the official website of Bahrain’s Ministry of Health, Bahrain’s official open innovation platform, and mivzaklive.co.il/index0.php.
- April 21: DDoS attack carried out against a website for designing and manufacturing advanced drones, a website regarding Israeli-Portuguese relations, the National Museum of Qatar, and Immergo.tv.
- April 22: DDoS attack carried out against the Qatar Digital Accessibility Center.
- April 23: DDoS attack carried out against a Pakistan real estate classified portal.
- April 24: DDoS attack carried out against an online platform for selling and managing insurance in Israel.
- April 28: DDoS attack carried out against site.xoox.co.il/hack-by-gorz-rostam.
- April 29: DDoS attack carried out against an educational ticketing and support system in Israel.
- May 5: Defacement of emomoro.com.
- May 7: DDoS attack carried out against dakscouriers.com.
- May 10: DDoS attack carried out against the Bahrain National Energy Commission.
- May 11: Defacement of mutalabah.com.
- May 12: DDoS attack carried out against moet.gov.ae and www.gov.il.
- May 15: DDoS attack carried out against the official Q&A portal of the Government of Qatar.
- May 18: DDoS attack carried out against apcofs.com and healthcarewaittime.com.
- May 19: DDoS attack carried out against secret.jo.
- May 20: DDoS attack carried out against the Saudi Ministry of Finance.
- May 21: DDoS attack carried out against kidoveyn.com.
- May 23: DDoS attack carried out against an independent public policy research institute in Israel, the secretariat of the Persian Gulf Cooperation Council, strangefactsabouttrhnegativebloodytypeorigin.com, and investturkana.geonta.com.
- May 24: DDoS attack carried out against guidestar.org.il.
- May 28: DDoS attack carried out against agento.az (an Azerbaijan real estate platform).
- June 1: DDoS attack carried out against the Constitutional Court of Azerbaijan and various Israeli embassies websites.
- June 4: The group released a message stating: “The time has come – we are Gorz Rostam striking back against the savage Zionist regime. We will not stop until this regime crumbles to dust.”
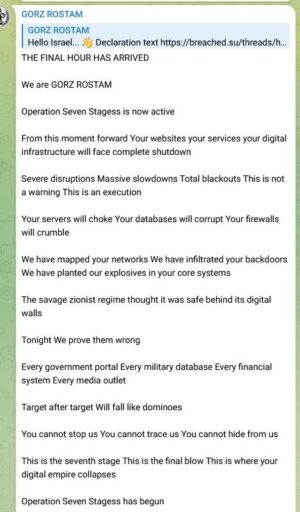
- June 7: The group announced “Operation Seven Stages” or “Operation Haft Khan” and carried out DDoS attacks against an Israeli center for local development and social cooperation, Geneva.il.us, and helekat.com.
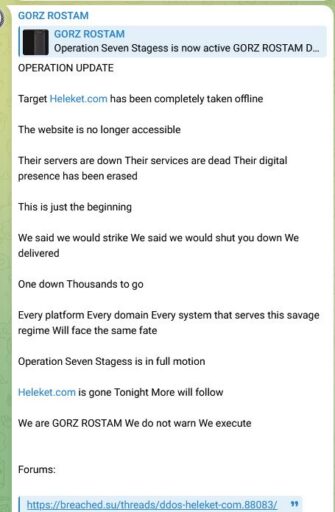
- June 8: The group confirmed that the website helekat.com was completely offline and no longer accessible.
- June 9: As part of “Operation Haft Khan,” a DDoS attack was carried out against the Israel Cyber Training Center.
- June 10: The group hacked the Pakistani hotel website pakrooms.com, extracting user identities and room maps. They also published a list of US Navy Commanders on the breached forums.
- June 11: Published login information for various Israeli internal websites and portals.
- June 14: Announced and executed DDoS attacks against several banks in Bahrain and the UAE.
- June 20: DDoS attack carried out against discountbank.co.il and fibi.co.il.
- June 27: DDoS attack carried out against modstore.in.
- June 28: DDoS attack carried out against stage.awnopy.com.au and cinestar.monamedia.net/news.
- June 30: DDoS attack and defacement carried out against mcdtaging.monsterdental.com, altraotticastore.evdpl.com, iyboutique.com, and jensproductsoftheworld.com.
- July 5: The group announced the successful disruption of banking systems across the Gulf region, including the Central Bank of Dubai.
- July 10: The group published a message on their telegram channel stating that the Mojahedin-e-Khalq are “puppets of the regime.” Following this the group carried out a DDoS attack against the Mojahedin website.
- July 13: Announced a DDoS attack carried out against Bahrain’s banking sector for the fourth time.
- July 14: The group opened an official data forum on the onion portal and announced the sale of top-secret military data relating to the BGM-109 Tomahawk Land Attack Missile.
- July 19: The group officially advertised their Telegram shop channel, featuring exploits, hacking tools, and zero-day vulnerabilities.
- July 24: Defacement of shopklub.com, demo.weblizar.com, and allegressebeauty.com.
- August 1: Defacement of ssv.ee.com, michpts.com, tacte.eu, shop-amazing.com, uaepcc.com/index.html, sultana-jo.com, and Saudi hosting.
- August 12: Defacement of flytomap.com, archlit.com, gasparglusberg.com, and flyingtech.in.
- August 14: The group announced that Operation Haft Khan had entered its second phase and advertised USA login details on their Telegram channel.
- August 18: DDoS attack and defacement carried out against harter-architekten.de, Warner Electronics, ingeidea.com, and eight other companies, featuring photos of children killed in the Minab strike.
- August 19: DDoS attack carried out against Emirates NBD bank.
- August 20: Advertised several Taiwanese databases.
- August 25: Defacement of medicdor.pl and poczta.11.a.pl (featuring a picture of Qasem Soleimani) and a defacement of basewood.pl with the message: “BLOOD FOR BLOOD WE KILL TRUMP.”
- August 26: Released a statement to the leaders of Saudi Arabia, Bahrain, UAE, Qatar, Egypt, Jordan, and Kuwait, claiming Donald Trump had been using them as “milking cows.”
- August 28: Published a text file containing numerous Israeli login details.
- August 29: DDoS attack carried out against Ivraeit, a private real estate development company based in Israel.
- September 2: Published a database list of the Taiwan government and related websites.
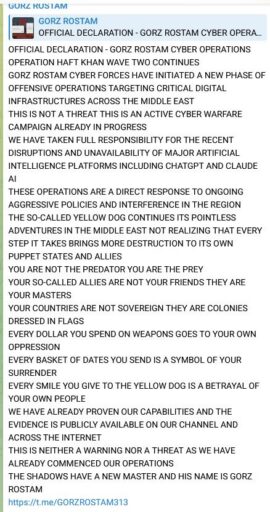
- September 3: Officially declared “Haft Khan Wave Two,” targeting critical digital infrastructure across the Middle East, and claimed responsibility for disrupting AI platforms including Claude and ChatGPT.
- September 5: DDoS attack carried out against Mekorot, Bahrain Electricity and Water Authority, Bahrain government services, government water and construction project tenders, Bahrain airport company, and IDE Technologies.
- September 6: DDoS attack carried out against AWWA and Veolia.
- September 16: The group issues a warning against all “websites and resources affiliated with Zionist propaganda.” The group then claim defacement of 13 Israeli websites.
Tactics/Techniques/Tradecraft/Procedures (TTP’s)
- DDoS attacks appear to be the groups most commonly used tactic as well as the use of defacement.
- The lack of technical evidence raises verification questions about the group. A key limitation in assessing the credibility of the groups claims is the absence of technical proof. Although the group post Check-Host reports and mirror links on their telegram, several of these are unvalidated by the mirror sites (e.g. zone-h and defacer). It is possible the group exaggerate claims to build reputation, psychological influence operations, or premature claims preceding real operation effect.
Sources:
Telegram
Undercodenews.com/uae-banking-disruption-claims-ignite-cybersecurity-alert-across-gulf-financial-sector-dark-web-recent-claims-video
Brinztech.com/breach-alerts/brinztech-middle-east-threat-update-adversial-log-aggressions-multi-vector-credential-stuffing-and-hacktivist-camouflage-the-gorz-rostam-operation-seven-khans-campaign
Imago.com/ar/en/technolgia/39570/cyber-alert-hacker-gorz-rostam-claims-to-leak-36-taiwanese-databases-including-justice-education-and-finance
https://defacer.id>archive>team=GORZ%ROSTAM>
issa-eg.org/threat-actor-claims-cyber-campaign-targeting-uae-banking-infrastructure
cyberxtron.com/resources/blogs/hacktivism-watch-june-2026-top-10-threat-actors-global-targeting-trends-7986
